Key Takeaways
Pocket Bitcoin confirmed a security breach exposed identity and wallet data for 291 users through partner bank correspondence.
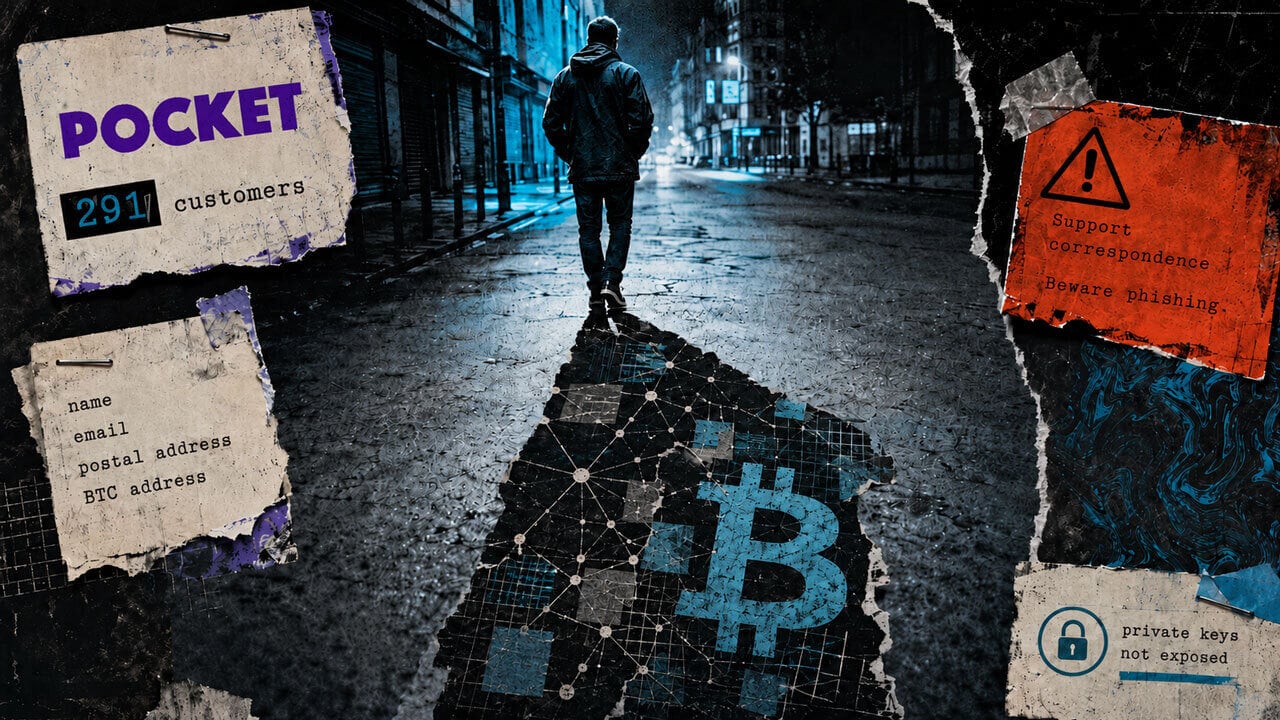
According to CryptoSlate, a data breach at Swiss non-custodial service Pocket Bitcoin exposed varying combinations of identity, location, and compliance data for 291 customers. An Aug. 31 update revealed that copied support correspondence with partner banks linked real-world names, postal addresses, and identity documents to public Bitcoin addresses and payment amounts.
CryptoSlate reported that while customer funds and private keys remained secure because private keys were never held by the non-custodial company, the exposed records create privacy, phishing, and physical-security risks. Pocket Bitcoin stated that its customer and transaction databases were not compromised, but related information was contained within stored support correspondence.
Every customer in the affected cohort received individual notices specifying which data fields were exposed. Pocket Bitcoin has concluded its forensic investigation, closed the vulnerability, filed a police report, and reported the incident to the Swiss Federal Data Protection and Information Commissioner. The company stated it has no indication of data misuse.
Source & Fact-Check Note
This report is synthesized from coverage by CryptoSlate. Information has been fact-checked and structured for market clarity by CoinQuickly’s research desk.
Read original article at CryptoSlate ↗